Healthcare
Hospital data center consolidation
How we would sequence a move of clinical systems into a new facility with HIPAA-aware handling and staged, after-hours cutovers.
Enterprise IT infrastructure migration
Secure, compliant, fully managed relocation and migration for enterprises, regulated industries, and colocation operators. We move production infrastructure with rollback paths, documented chain of custody, and a plan for zero-downtime cutover — with domestic and international shipping handled end to end.
We reply to every inquiry — typically within one business day.
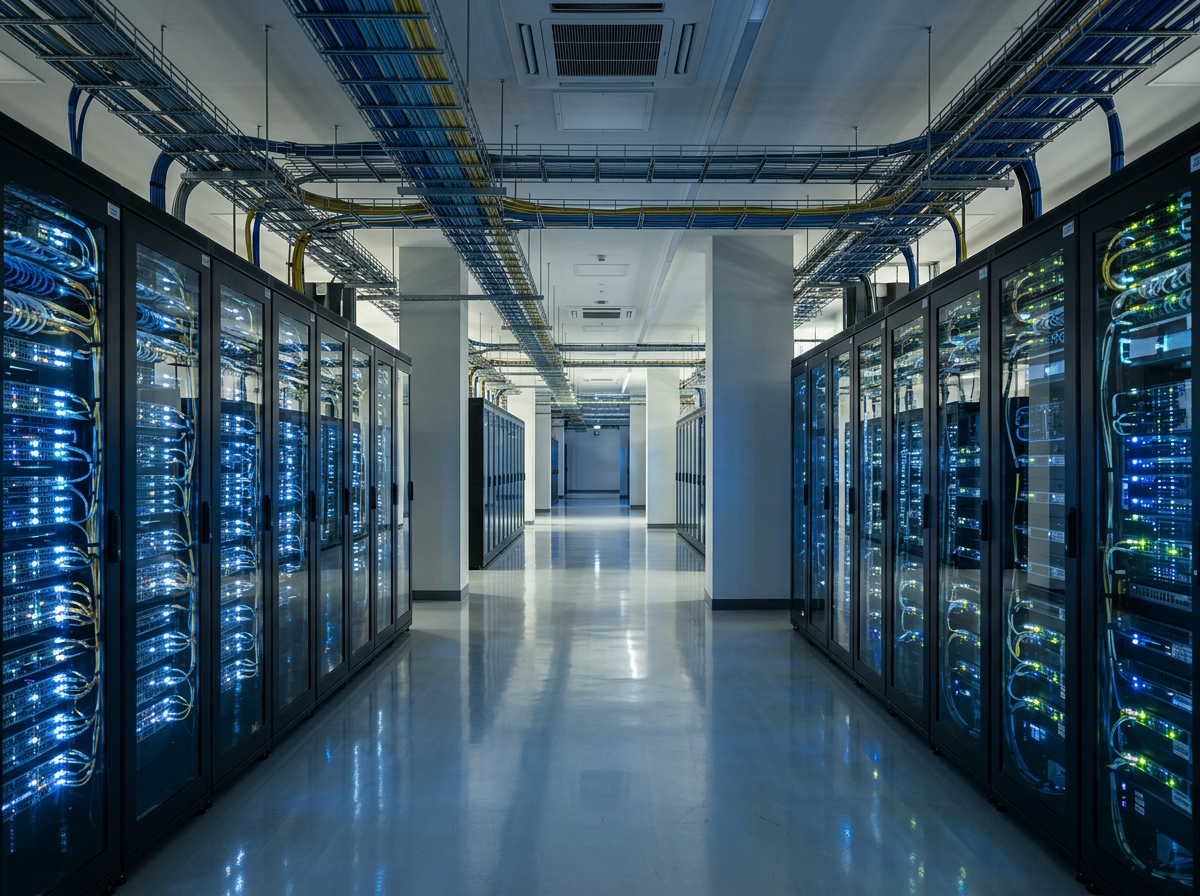
Phased cutovers
Rollback paths planned before anything is unracked.
Audit-grade records
Documentation and chain of custody on every asset.
Zero-downtime planning
Migration sequenced to protect production systems.
What we do
One accountable team from discovery through cutover — so dependencies, sequencing, and risk are owned in one place.
Full-facility moves and consolidations, sequenced to protect production systems with tested rollback paths.
De-rack, transport, and re-rack of servers, storage, and network gear with labeled, documented handling.
Cutovers between facilities and colocation providers, with cabling, IP, and connectivity planned in advance.
Insured, chain-of-custody transport for sensitive and regulated hardware, tracked end to end.
Structured teardown, media handling, and disposition documentation for retired infrastructure.
Discovery, dependency mapping, and phased runbooks so every cutover has an owner and a checkpoint.
Coordinated freight for equipment moves across the country or across borders, with customs paperwork and insured, tracked handling.
Where we move you
The same planning discipline, chain of custody, and documentation standard whether the destination is across the state or across an ocean.
Step 1
Assessment & export planning
Step 2
Crating & documentation
Step 3
Air/ocean transit with tracking
Step 4
Customs clearance & re-install
How we work
We plan like an engineering program: dependencies mapped, cutovers staged, and a rollback path ready before anything leaves the rack.
We inventory hardware, applications, and interdependencies so nothing moves before its dependencies are understood.
Every phase gets a sequenced runbook with checkpoints, owners, and a documented rollback path.
We migrate in phases, validating each stage against acceptance criteria before proceeding to the next.
Post-move validation, audit-grade documentation, and a clean handover to your operations team.
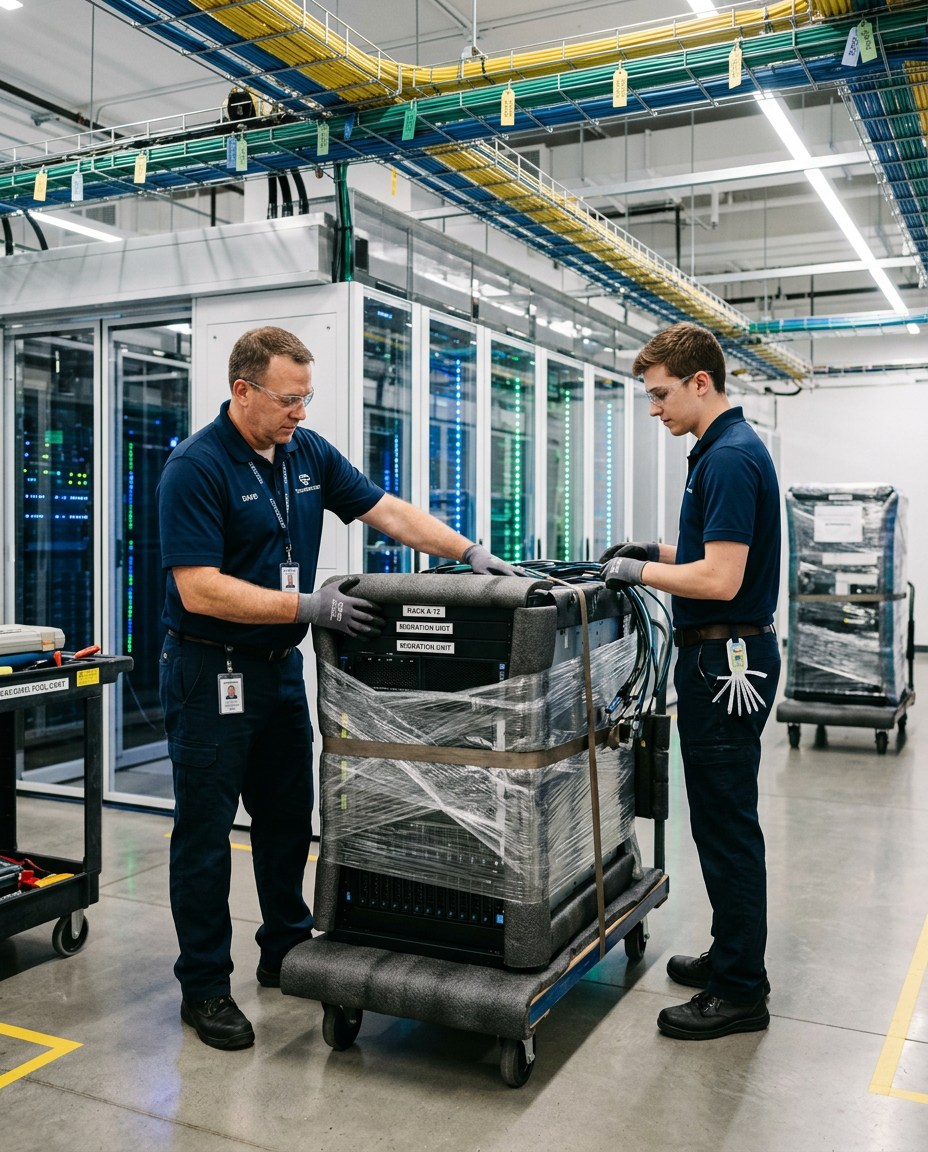
Compliance posture
We align our processes with the frameworks our clients answer to, so a move never becomes a compliance gap.
Procedures designed for environments with protected health information, including access control and documented handling.
Operational controls modeled on SOC 2 principles for security, availability, and confidentiality.
Every asset is tracked from de-rack to re-rack, with custody recorded at each transfer.
Runbooks, asset logs, and verification records you can hand to auditors and stakeholders.
Note: References to HIPAA and SOC 2 describe our operational practices and process alignment. They are not a claim of certification. We are glad to walk your security and compliance teams through our controls during procurement.
Sample project approach
The scenarios below illustrate how we plan and sequence work. They describe our methodology, not specific client engagements. We're happy to provide references during procurement.
Healthcare
How we would sequence a move of clinical systems into a new facility with HIPAA-aware handling and staged, after-hours cutovers.
Financial services
A sample approach for migrating trading and back-office infrastructure between colocation providers with documented chain of custody.
Enterprise
How we would combine several regional server rooms into a single facility using dependency mapping and phased runbooks.
Where we work
We run relocations across the continental United States, with active programs in major data center and colocation markets.
Tell us about your environment and timeline. We reply to every inquiry — typically within one business day — and can walk your security and compliance teams through our process.
Common questions